

AML/CTF Program Guide: AUSTRAC Compliance and Transitional Rules 2026

Australia's anti-money laundering and counter-terrorism financing (AML/CTF) framework has undergone significant reforms, introducing stronger expectations for governance, customer due diligence and financial crime risk management.
With the updated requirements now in force, financial institutions and other reporting entities face a critical challenge: ensuring their AML/CTF programs remain compliant, effective and responsive to emerging threats.
While certain transitional arrangements extend into 2029 and 2030, businesses must continue strengthening their risk assessments, monitoring controls and compliance practices.
For banks, fintechs and other regulated businesses, effective AML compliance requires more than documented policies. It demands risk-based controls that can identify suspicious activity, adapt to emerging threats and withstand regulatory scrutiny.
This guide explains how to develop and maintain an effective AML/CTF program, meet AUSTRAC's current compliance requirements and navigate the transitional rules that continue to shape Australia's regulatory landscape.
What Is an AML/CTF Program Under AUSTRAC?
An AML/CTF program is a documented, risk-based framework designed to help reporting entities identify, assess, manage and mitigate money laundering, terrorism financing and proliferation financing risks.
Under Australia's AML/CTF Act 2006, reporting entities must maintain an AML/CTF program appropriate to the nature, size and complexity of their business.
An effective program contains two essential components:
- Financial crime risk assessment: Identifies and evaluates the money laundering, terrorism financing and proliferation financing risks the business may reasonably face.
- AML/CTF policies: Establish the procedures, systems and controls used to manage those risks and fulfil regulatory obligations.
The program must be documented, approved by a senior manager and implemented in daily operations. It must also be reviewed and updated as circumstances change.
AUSTRAC emphasises a risk-based approach, meaning compliance controls must reflect the specific risks of each business.
For example, a fintech processing instant cross-border payments may face different threats from a bank offering corporate banking services. Their monitoring controls, customer due diligence procedures and risk assessments should reflect those differences.
Who Must Maintain an AML/CTF Program in Australia?
Businesses providing designated services under the AML/CTF Act generally need to maintain an AML/CTF program, subject to applicable exemptions and special arrangements.
These include banks, credit providers, remittance providers, payment businesses and certain virtual asset service providers.
Australia's expanded regulatory framework also covers designated services commonly provided by:
- Lawyers and legal professionals
- Accountants and conveyancers
- Real estate professionals
- Trust and company service providers
- Dealers in precious metals and stones
- Additional virtual asset service providers
These newly regulated sectors are often referred to as Tranche 2 entities.
However, regulation depends on the specific designated services provided, not simply a business's professional classification.
Existing reporting entities must ensure their AML/CTF programs align with the current framework, while newly regulated businesses must implement appropriate controls for their designated services.
How to Develop an Effective AML/CTF Program: Five Essential Steps
Building an effective AML/CTF program involves establishing accountability, understanding financial crime exposure, implementing appropriate controls and evaluating their effectiveness.
AUSTRAC's guidance outlines five essential steps.
Step 1: Establish Strong AML/CTF Governance
Effective AML compliance begins with clear responsibilities and management oversight.
Reporting entities must identify their governing body, appoint an AML/CTF compliance officer and establish appropriate senior management responsibilities.
The governing body oversees the organisation's management of financial crime risks, while the compliance officer coordinates day-to-day AML/CTF activities.
Businesses should establish reporting lines, escalation procedures, staff training and personnel due diligence.
Governance arrangements must also ensure compliance teams have sufficient authority and resources to perform their responsibilities.
Without clear accountability, financial crime risks can remain unresolved even when detection systems are in place.
Step 2: Conduct a Comprehensive Risk Assessment
The risk assessment forms the foundation of an effective AML/CTF program.
Reporting entities must assess their exposure to money laundering, terrorism financing and proliferation financing based on factors such as:
- Customer types and characteristics
- Products and designated services
- Geographic exposure
- Delivery channels
- Emerging financial crime methods
For example, a digital payments provider may face risks involving money mule networks, rapid fund movements and unusual transaction patterns.
A bank handling international payments may face additional exposure to complex ownership structures and cross-border laundering.
Risk assessments should consider the nature and seriousness of potential threats and how criminals might exploit the business.
They must also be revisited when significant changes occur, including the introduction of new products, customer segments or technologies.
Step 3: Develop Risk-Based AML/CTF Policies and Controls
Once financial crime risks have been assessed, businesses must establish policies and controls to manage them.
These should address customer due diligence, transaction monitoring, suspicious matter reporting, record-keeping, staff training and escalation procedures.
Controls should be proportionate to identified risks.
For instance, higher-risk customers may require enhanced due diligence and additional monitoring.
Similarly, transaction monitoring should consider customer behaviour, transaction patterns and emerging financial crime typologies rather than relying exclusively on fixed thresholds.
An effective approach connects each significant risk with appropriate preventive or detective controls.
Businesses should document how those controls operate, who is responsible for them and how their effectiveness will be assessed.
Step 4: Review and Update the AML/CTF Program
Financial crime threats evolve continuously, making regular program reviews essential.
Under AUSTRAC's current framework, reporting entities must review their AML/CTF risk assessments and policies at least once every three years, with earlier reviews required when specified circumstances arise.
These may include significant changes to products, customer types, delivery channels, geographic exposure or emerging technologies.
Reviews may also be triggered by adverse independent evaluation findings or relevant information communicated by AUSTRAC.
Updates must receive appropriate approval and be documented within the required timeframe, including the 14-day documentation requirement.
For financial institutions, reviewing transaction monitoring scenarios and thresholds is particularly important.
A control designed around historical transaction behaviour may become less effective when criminals adopt new laundering techniques.
Regular testing helps institutions assess whether controls remain aligned with their actual risk exposure.
Step 5: Conduct Independent Evaluations
Independent evaluations help reporting entities determine whether their AML/CTF programs are appropriately designed and implemented.
These evaluations examine risk assessments, AML/CTF policies, compliance with regulatory requirements and the effectiveness of risk management arrangements.
Under the current framework, independent evaluations must generally occur at least once every three years, subject to applicable transitional arrangements.
The evaluator must prepare a written report documenting findings, which is provided to the governing body and relevant senior manager.
Where deficiencies are identified, businesses should prioritise remediation and update their controls accordingly.
Independent evaluations should therefore be treated as opportunities to strengthen financial crime prevention, rather than merely as compliance exercises.
AUSTRAC AML/CTF Transitional Rules 2026 Explained
Australia's AML/CTF Transitional Rules 2026 provide arrangements to help reporting entities implement selected changes introduced under the reformed regulatory framework.
Although the broader reforms are already in effect, several transitional provisions remain active.
These arrangements give eligible organisations additional time to update customer identification procedures, reporting systems and independent evaluation schedules.
However, transitional rules do not exempt reporting entities from their ongoing AML compliance obligations.
Businesses must understand which requirements already apply and which are subject to specific transitional provisions.
Key AUSTRAC Transitional Deadlines Still Relevant in 2026
Several transitional deadlines remain important for reporting entities navigating Australia's updated AML/CTF framework. Eligible existing entities can continue using applicable customer identification procedures for specified customer classes until 30 March 2029. For existing reporting entities enrolled on 30 March 2026 that completed at least one independent review under the previous rules, the first independent evaluation must be conducted by the later of 31 March 2027 or four years after their most recent review.
Newly regulated businesses have staggered first independent evaluation deadlines between 2029 and 2030, depending on their AUSTRAC account numbers. Additionally, the standard transition from international funds transfer instruction (IFTI) reporting to international value transfer service (IVTS) reporting is scheduled for 31 March 2029, subject to permitted alternative dates.
These deadlines provide a practical planning framework, although the precise requirements depend on each organisation's regulatory status and transitional eligibility.
Transitioning from ACIP to Initial Customer Due Diligence
One important transitional arrangement concerns customer identification.
Eligible reporting entities enrolled with AUSTRAC on 30 March 2026 may continue using applicable customer identification procedures (ACIP) for specified customer classes during the transitional period ending 30 March 2029.
To rely on this arrangement, businesses were required to document the relevant customer classes and their intended transition dates in their AML/CTF policies by 1 July 2026.
This arrangement applies specifically to the transition from ACIP to the updated initial customer due diligence framework.
Importantly, the updated ongoing customer due diligence obligations are already in force.
Businesses must therefore distinguish between deferred initial identification requirements and ongoing monitoring responsibilities.
Institutions should use the remaining transitional period to assess onboarding procedures, update verification processes and ensure a structured migration to the new framework.
Independent Evaluation Deadlines
The transitional framework also provides additional time for certain reporting entities to conduct their first independent evaluation under the reformed requirements.
For existing reporting entities enrolled on 30 March 2026 that completed at least one independent review under the previous rules, the first independent evaluation must be conducted by the later of:
- 31 March 2027, or
- Four years after their most recent independent review.
For eligible newly regulated businesses, first independent evaluation deadlines are staggered between June 2029 and December 2030 according to their AUSTRAC account numbers.
These transitional arrangements affect the first evaluation deadline. Reporting entities must also establish an appropriate ongoing evaluation frequency in their AML/CTF policies.
Businesses should confirm their applicable deadlines, review previous evaluation records and ensure their schedules are appropriately documented.
Transition to International Value Transfer Reporting
The reforms also introduce changes to international value transfer reporting.
Under the transitional arrangements, applicable reporting entities continue submitting international funds transfer instruction (IFTI) reports until their transition to the international value transfer service (IVTS) reporting framework.
The standard transition date is 31 March 2029, although eligible entities may nominate a permitted substitute date up to 30 September 2029.
Businesses should use the transitional period to assess reporting systems, data requirements and operational readiness.
For further information, refer to AUSTRAC's AML/CTF Transitional Rules 2026.
What Reporting Entities Should Prioritise Now
Rather than focusing only on when reforms commenced, institutions should assess whether their existing AML/CTF arrangements remain effective.
Current priorities include strengthening customer risk assessments, validating transaction monitoring controls, reviewing customer due diligence processes and confirming independent evaluation schedules.
Where transitional provisions apply, businesses should maintain documented implementation plans with clear responsibilities and milestones.
The objective is not simply to meet future deadlines, but to ensure compliance controls remain effective throughout the transition.
Key AML Compliance Obligations for Reporting Entities
Beyond maintaining an AML/CTF program, reporting entities must fulfil several ongoing regulatory responsibilities.
Customer Due Diligence and Monitoring
Customer due diligence involves identifying customers, verifying relevant information, assessing financial crime exposure and monitoring relationships over time.
Enhanced due diligence may be necessary when customers, activities or transactions present higher risks.
Ongoing monitoring should identify suspicious or unusual activity inconsistent with expected customer behaviour.
Regulatory Reporting
Depending on their designated services, reporting entities must submit applicable reports to AUSTRAC.
These include:
- Suspicious Matter Reports (SMRs): Required when a reporting entity forms a suspicion on reasonable grounds. Reporting deadlines generally depend on the nature of the suspicion.
- Threshold Transaction Reports (TTRs): Required for covered transfers involving AUD 10,000 or more in physical currency, or the foreign currency equivalent.
- International transfer reports: Relevant IFTI or IVTS reporting obligations apply according to the legislation and transitional arrangements.
Accurate and timely reporting helps AUSTRAC analyse suspicious financial activity and support law enforcement investigations.
Record-Keeping
Reporting entities must retain required records relating to customer identification, transactions, compliance activities and regulatory reporting.
Many transaction-related records must generally be retained for at least seven years, although the precise retention period depends on the record type.
Maintaining accurate, accessible documentation is essential for demonstrating AML compliance.
Common AML/CTF Program Mistakes to Avoid
Even established financial institutions can develop gaps between documented compliance policies and operational practices.
Outdated risk assessments: Failing to reassess exposure when products, customer behaviour or criminal methods change.
Static monitoring controls: Relying on scenarios and thresholds that have not been tested against emerging financial crime patterns.
Weak governance: Unclear responsibilities, ineffective escalation procedures and insufficient management oversight.
Inadequate documentation: Failing to maintain evidence of investigations, monitoring decisions and changes to controls.
Delayed remediation: Identifying weaknesses through independent evaluations without implementing timely improvements.
An effective AML/CTF program should address these weaknesses through continuous monitoring, testing and management oversight.
How Collective Intelligence Strengthens AML/CTF Compliance
Financial crime is a network problem.
Criminal networks move across institutions, products and jurisdictions, often adapting faster than individual organisations can respond.
Yet many financial institutions develop detection strategies primarily from activity observed within their own environments.
This creates a significant limitation. An institution may encounter a new financial crime pattern before its monitoring controls are equipped to recognise it.
Collective intelligence helps broaden that perspective.
By drawing on financial crime typologies, risk patterns and emerging threat insights identified across multiple institutions, compliance teams can strengthen their understanding of potential vulnerabilities.
However, intelligence alone is insufficient.
It must be translated into practical controls that can be tested, refined and deployed within an institution's environment.
Testing detection scenarios, evaluating thresholds and simulating potential impact can help organisations adapt their controls while managing unnecessary alerts.
For AML compliance teams, the objective is to move beyond simply identifying emerging threats towards responding to them with greater confidence.
How Tookitaki Turns Intelligence into Financial Crime Control
Tookitaki is the intelligence ecosystem, helping financial institutions prevent, detect, adapt and stay ahead of emerging financial crime threats.
Its Anti-Financial Crime (AFC) Ecosystem brings together real-world typology intelligence, risk patterns and emerging threat insights from financial crime professionals and participating institutions.
This collective intelligence helps institutions learn from threats observed across the wider financial ecosystem, rather than relying exclusively on patterns encountered within their own operations.
Tookitaki's FinCense platform turns this intelligence into operational controls.
By combining AI with intelligence from the AFC Ecosystem, FinCense helps institutions test scenarios, recommend thresholds, simulate impact and translate emerging risk patterns into deployable controls.
For institutions strengthening their AML/CTF programs, this approach supports adaptive transaction monitoring, customer risk management and investigation workflows.
The result is a stronger connection between financial crime intelligence and day-to-day compliance operations, helping institutions identify threats sooner, adapt controls faster and respond with greater confidence.
Collective intelligence. Confident crime control.
Frequently Asked Questions
What is an AML/CTF program?
An AML/CTF program is a documented framework that identifies money laundering, terrorism financing and proliferation financing risks and establishes policies and controls to manage them.
What are AUSTRAC's current AML/CTF program requirements?
Reporting entities must maintain appropriate risk assessments, AML/CTF policies, governance arrangements, customer due diligence processes, reporting procedures and independent evaluation mechanisms.
What are the AUSTRAC AML/CTF Transitional Rules 2026?
The transitional rules establish specific arrangements and deadlines to help eligible reporting entities implement selected regulatory changes, including customer identification, international transfer reporting and independent evaluations.
How often must an AML/CTF program be reviewed?
Risk assessments and AML/CTF policies must generally be reviewed at least once every three years and earlier when relevant triggers occur. Independent evaluations are also generally required at least every three years, subject to transitional arrangements.
Can AML technology guarantee AUSTRAC compliance?
No. Technology can support monitoring, risk assessment and investigations, but reporting entities remain responsible for implementing effective controls and meeting their regulatory obligations.
Conclusion: Building AML/CTF Programs That Adapt to Emerging Risks
Australia's reformed AML/CTF framework reinforces the importance of effective governance, risk-based controls and continuous compliance improvement.
Reporting entities must understand their financial crime exposure, implement appropriate safeguards and ensure their programs evolve alongside changing threats.
While transitional arrangements provide additional time to implement selected changes, effective compliance requires ongoing attention to control performance.
As financial crime increasingly crosses institutional and geographic boundaries, organisations also need access to intelligence beyond their own experiences.
By combining strong governance, regulatory compliance and collective financial crime intelligence, institutions can build AML/CTF programs that remain effective as threats evolve.
Tookitaki's intelligence ecosystem, together with FinCense, helps translate that intelligence into practical financial crime controls, enabling institutions to identify threats sooner, adapt faster and respond with greater confidence.
Discover how Tookitaki and FinCense can help your institution turn financial crime intelligence into stronger, more adaptive controls. Talk to our team.
Experience the most intelligent AML and fraud prevention platform
Experience the most intelligent AML and fraud prevention platform
Experience the most intelligent AML and fraud prevention platform
Top AML Scenarios in ASEAN
The Role of AML Software in Compliance
Talk to an Expert
Our Thought Leadership Guides
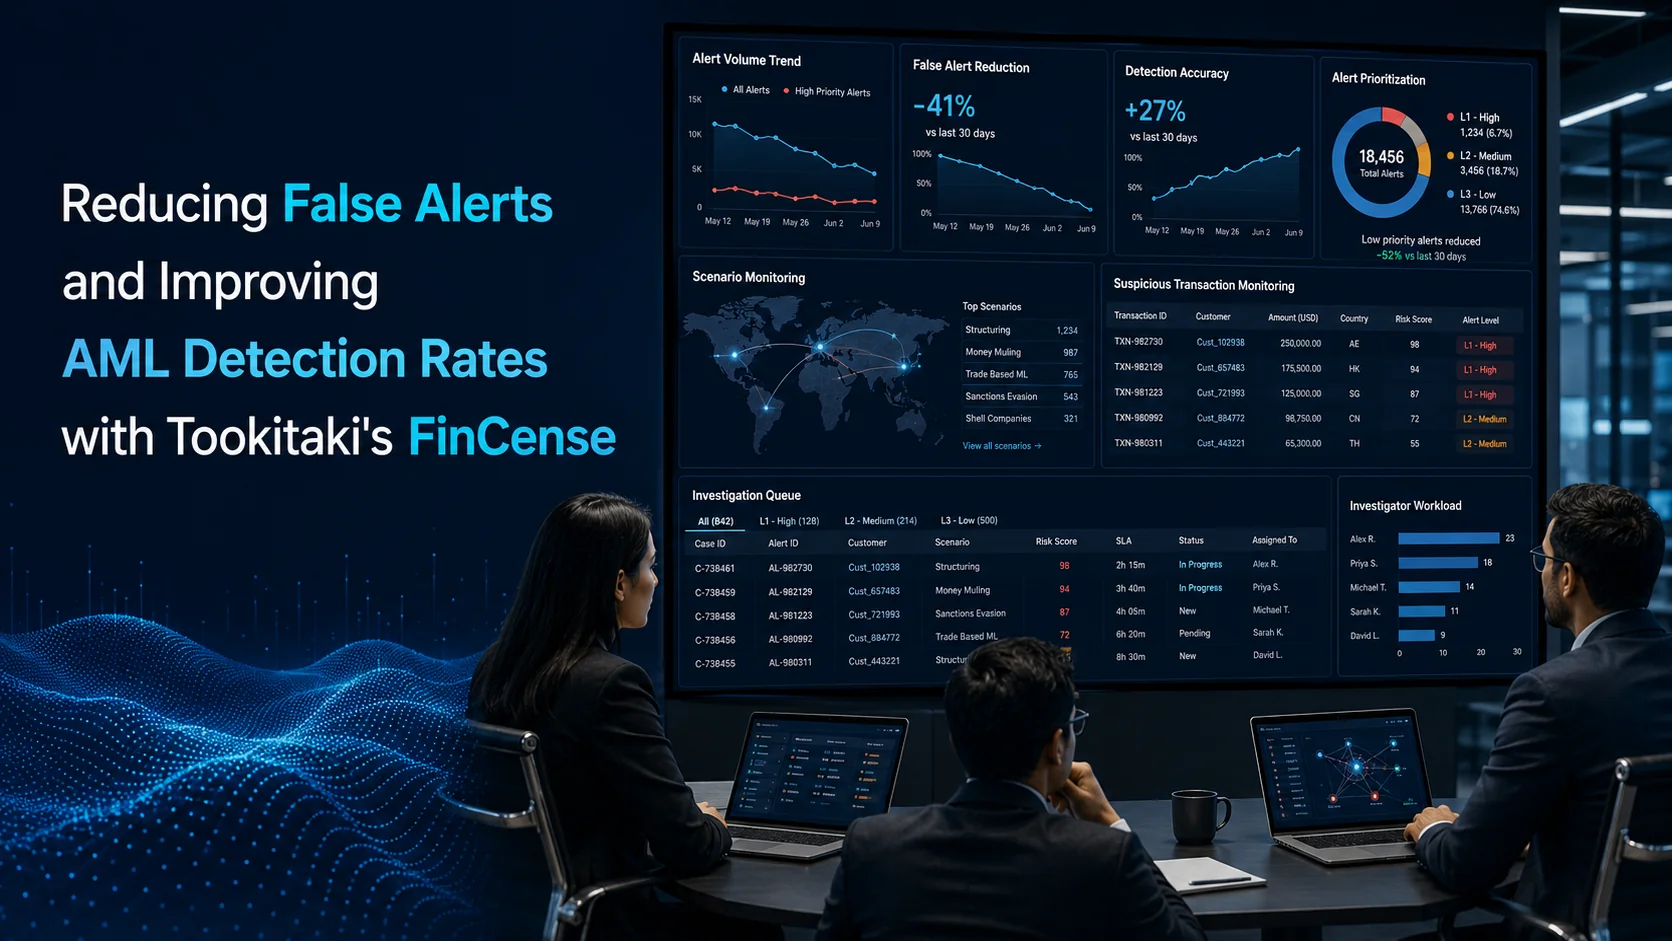
Reducing False Alerts and Improving AML Detection Rates with Tookitaki's FinCense
False positives overwhelm AML compliance teams while genuine financial crime goes undetected. Tookitaki addresses this two ways: an Alert Prioritization AI Agent that works on top of any legacy system, and FinCense Transaction Monitoring with scenario-based detection and automated threshold tuning.
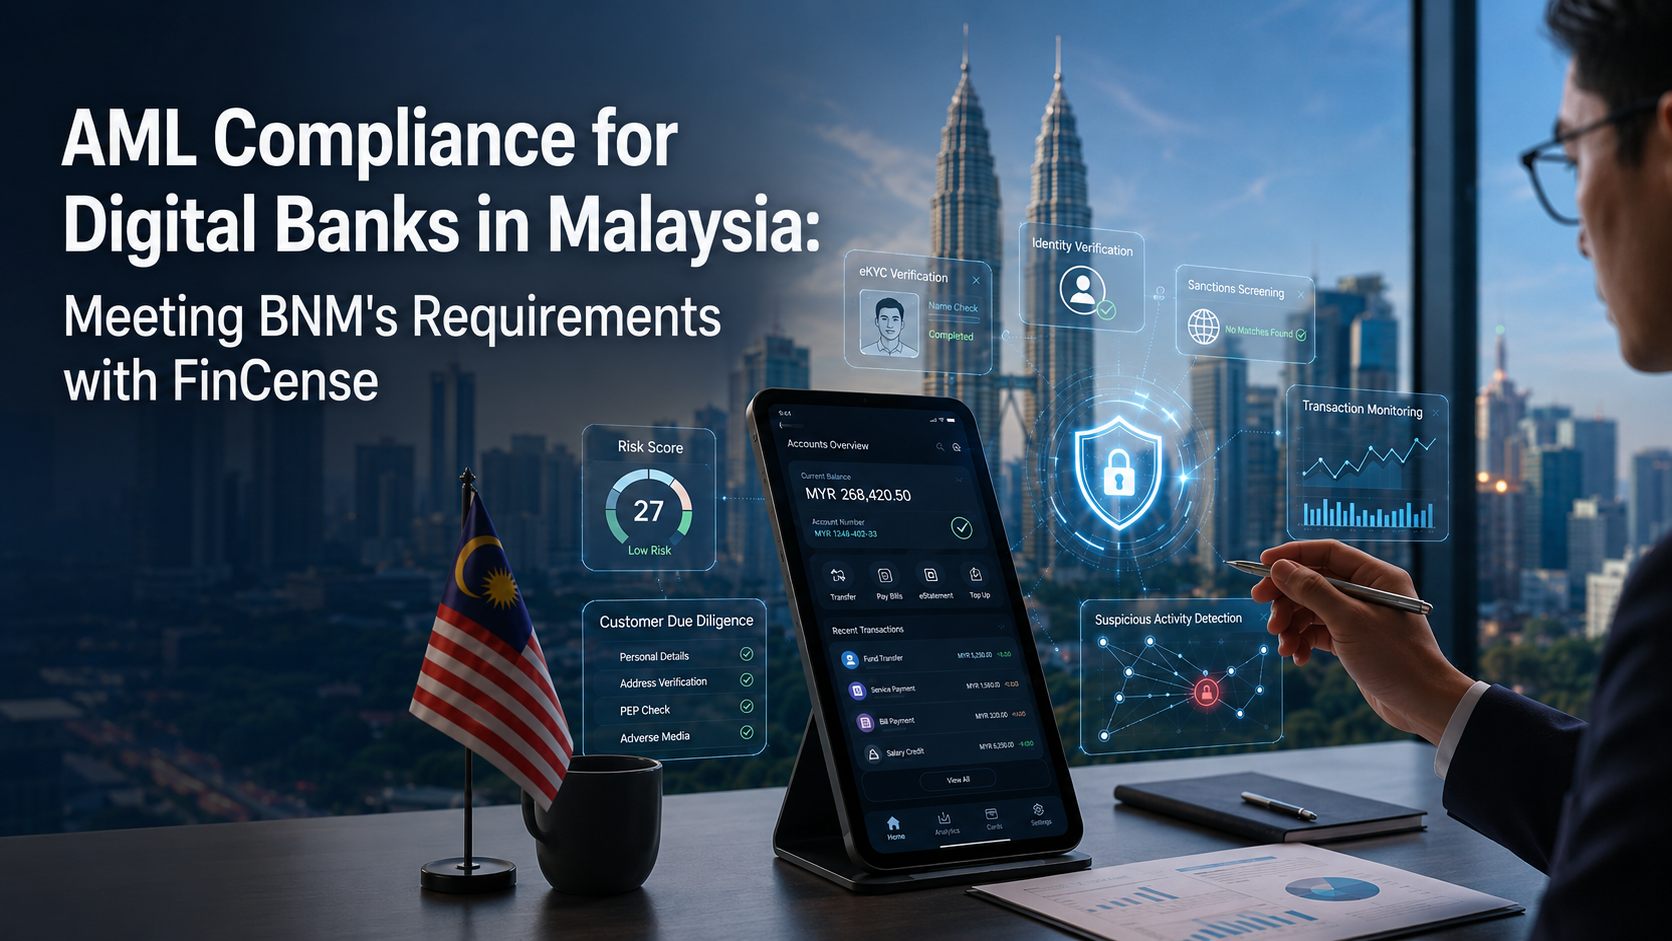
AML Compliance for Digital Banks in Malaysia: Meeting BNM's Requirements with FinCense
Malaysia's digital banks face BNM's 2023 AML/CFT Policy Document, FATF's updated recommendations, and mounting pressure on eKYC and transaction monitoring standards. Here is how FinCense addresses these requirements.

Living Under the STR Clock: The Growing Pressure on AML Investigators
AML investigators face increasing pressure to make Suspicious Transaction Report decisions under tight timelines and growing alert volumes. Explore the challenges behind STR reporting and the shift toward intelligence-led investigations.

